Wrap Up
Table of Contents
1. The Final Architecture
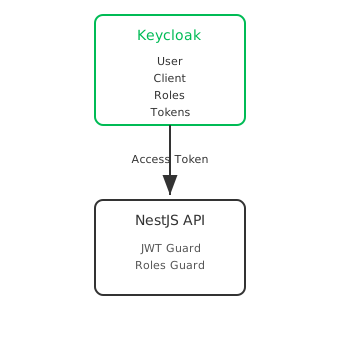
Every request into the NestJS API now travels the same path: User → Keycloak (authenticate) → Access Token → NestJS API → JWT Guard → Roles Guard → Response. That's the one idea worth keeping from this whole hour: Keycloak isn't a pile of screens to memorize — it's a single consistent flow, with your API trusting a token instead of ever handling a password.
2. Recap
| Term | What it means | Covered in |
|---|---|---|
| Realm | An isolated tenant of users, clients, and roles | Part 2, Part 3 |
| User | An account inside a realm | Part 2, Part 4 |
| Client | An application registered against a realm | Part 2, Part 4 |
| Roles | What a user is allowed to do | Part 2, Part 7 |
| OAuth 2.0 | Protocol for authorization — how a token is obtained | Part 2 |
| OpenID Connect | Identity layer on top of OAuth 2.0 — adds authentication | Part 2 |
| Authorization Code | The short-lived code exchanged for tokens | Part 5 |
| Access Token | Proves authentication; sent with every API request | Part 2, Part 6 |
| Refresh Token | Used to get a new access token without logging in again | Part 2 |
| ID Token | Describes who the user is | Part 2 |
| JWT | The encoded format tokens are issued in | Part 6 |
| Authentication | "Who are you?" | Part 1 |
| Authorization | "What are you allowed to do?" | Part 1 |
| API protection | Validating a token, then checking its roles | Part 7 |
3. What We Deliberately Skipped
This was a 1-hour crash course, not the whole product. Left out on purpose, each worth its own dedicated deep dive:
- LDAP integration — syncing against an existing corporate directory
- Google / GitHub identity providers — social login
- Custom themes — branding the login pages
- User federation — beyond LDAP, other external user stores
- Fine-grained authorization — resource- and permission-based authorization services, beyond simple realm roles
- Keycloak clustering / high availability
- Custom SPI / providers — extending Keycloak's own behavior
- Kubernetes deployment
- Production security hardening — real databases, HTTPS, hostname
configuration (everything
start-devskips) - Advanced token customization — custom claims, token exchange
If you want to go deeper on the NestJS side of this stack, the companion NestJS Crash Course series covers building the rest of a production-style API — this crash course's reference implementation is deliberately built to drop straight into that project's structure.
Buy Me a Coffee
Found this tutorial helpful? Consider buying me a coffee to support more free content!